OceanBase
English日本語简体中文
Docs Home
Products
Integrations
Release Notes

Databases

OceanBase DatabaseOceanBase Cloud OceanBase Best Practices

Tools

OceanBase Cloud PlatformOceanBase Migration ServiceOceanBase Developer CenterOceanBase Migration AssessmentOceanBase Admin ToolOceanBase Loader and DumperOceanBase DeployerKubernetes operator for OceanBaseOceanBase Diagnostic Tool OceanBase Binlog Service

Connectors and Middleware

OceanBase Database Proxy OceanBase Connector/C OceanBase Connector/J OceanBase Connector/ODBC OceanBase Connector/NETOceanBase Command-Line Client

Databases

OceanBase DatabaseOceanBase Cloud OceanBase Best Practices

Connectors and Middleware

OceanBase Database Proxy OceanBase Connector/C OceanBase Connector/J OceanBase Connector/ODBC OceanBase Connector/NETOceanBase Command-Line Client

Tools

OceanBase Cloud PlatformOceanBase Migration ServiceOceanBase Developer CenterOceanBase Migration AssessmentOceanBase Admin ToolOceanBase Loader and DumperOceanBase DeployerKubernetes operator for OceanBaseOceanBase Diagnostic Tool OceanBase Binlog Service
OceanBase DatabaseOceanBase Cloud ToolsConnectors and MiddlewareLifecycle Support Policy

OceanBase Developer Center

V4.4.2
  • Topics Overview
  • Overview
    • What is ODC?
    • Features
    • Architecture
    • Limitations
    • ODC console
  • Quick Start
    • Client ODC
      • Overview
      • Install Client ODC
      • Use Client ODC
    • Web ODC
      • Overview
      • Deploy Web ODC
      • Use Web ODC
  • Data Source Management
    • Create a data source
    • Data sources and project collaboration
    • Database O&M
      • Session management
      • Global variable management
      • Recycle bin management
  • SQL Development
    • Edit and execute SQL statements
    • Perform PL compilation and debugging
    • Use the command-line window
    • Edit and export the result set
    • Execution analysis
    • Generate test data
    • System settings
    • Intelligent SQL development
    • Common features
    • Database objects
      • Table objects
        • Overview
        • Create a table
      • View objects
        • Overview
        • Create a view
        • Manage views
      • Materialized view objects
        • Overview
        • Create a materialized view
        • Manage materialized views
      • Function objects
        • Overview
        • Create a function
        • Manage functions
      • Stored procedure objects
        • Overview
        • Create a stored procedure
        • Manage stored procedures
      • Sequence objects
        • Overview
        • Create a sequence
        • Manage sequences
      • Package objects
        • Overview
        • Create a program package
        • Manage program packages
      • Trigger objects
        • Overview
        • Create a trigger
        • Manage triggers
      • Type objects
        • Overview
        • Create a type
        • Manage types
      • Synonym objects
        • Overview
        • Create a synonym
        • Manage synonyms
      • External resource objects
        • External resources
        • Create an external resource
        • Manage external resources
  • Database Change Risk Management
    • Project collaborative management
      • Project management
      • Manage databases
      • Manage logical databases
      • Add object storage files
      • Manage project members
      • Desensitize data
      • Notification management
        • Overview
        • View notification records
        • Manage notification channels
          • Create a notification channel
          • View, edit, and delete a notification channel
          • Configure a custom channel
        • Manage notification rules
    • Manage user permissions
      • Users and roles
      • Automatic authorization
      • Apply for project permissions
      • Apply for database permissions
      • Apply table/view permissions
    • Security standards
      • Environment configuration
        • SQL check specifications
        • SQL window specification
      • Risk Management
        • Overview
        • Manage risk identification rules
        • Manage approval processes
      • Desensitization algorithms
      • Operation audit
  • Ticket Management
    • Import schemas and data
    • Export schemas and data
    • Database change management
    • Manage changes to logical databases
    • Batch database change management
    • Online schema changes
    • Synchronize shadow tables
    • Schema comparison
  • Data Lifecycle Management
    • Data archiving
    • Data cleanup
    • Manage partitioning plans
      • Manage partitioning plans
      • Set partitioning strategies
      • Examples of partitioning strategies
    • SQL Plan
  • System Integration
    • Login integration
    • Approval integration
    • SQL approval integration
    • Bastion host integration
    • Integrate with LLMs
  • Deployment Guide
    • Deployment overview
    • Preparations before deployment
    • Deploy ODC in single-node mode
    • Deploy ODC in high-availability mode
    • Deployment verification
  • Upgrade Guide
    • Upgrade Overview
    • Preparations for upgrade
    • Update single-node ODC
    • Update high-avaliability ODC
    • Upgrade verification
    • Rollback after upgrade failed
  • Best Practices
    • Tips for SQL development
    • Explore ODC team workspaces
    • Understanding real-time SQL diagnostics for OceanBase AP
    • OceanBase historical database solutions
    • ODC SQL check for automatic identification of high-risk operations
    • Integration with ODC enterprise-level account system
    • Manage and modify sharded databases and tables via ODC
    • Data masking and control practices
    • Enterprise-level control and collaboration: Safeguard every database change
  • Troubleshooting
    • ODC troubleshooting process
    • Collect message
      • View the runtime environment and version information
      • View web ODC logs
      • View client ODC logs
      • View end-to-end ODC-related logs
      • View ODC MetaDB data
      • Query the index status in OceanBase Database V4.x
      • Query the index status in OceanBase Database V1.4.x to V3.2.x
      • Collect JVM runtime information
      • Use tcpdump to capture packets
    • FAQ
      • Installation of client ODC
      • Web ODC deployment and startup
      • Connection Information
      • Command-line window
      • DDL statement display
  • Release Notes
    • V4.4
      • ODC V4.4.0
      • ODC V4.4.1
      • ODC V4.4.2
    • V4.3
      • ODC V4.3.4
      • ODC V4.3.3
      • ODC V4.3.2
      • ODC V4.3.1
      • ODC V4.3.0
    • V4.2
      • ODC V4.2.4
      • ODC V4.2.3
      • ODC V4.2.2
      • ODC V4.2.1
      • ODC V4.2.0
    • V4.1
      • ODC V4.1.3
      • ODC V4.1.2
      • ODC V4.1.1
      • ODC V4.1.0
    • V4.0
      • ODC V4.0.2
      • ODC V4.0.0
    • V3.4
      • ODC V3.4.0
    • V3.3
      • ODC V3.3.3
      • ODC V3.3.2
      • ODC V3.3.1
      • ODC V3.3.0
    • V3.2
      • ODC V3.2.3
      • ODC V3.2.2
      • ODC V3.2.1
      • ODC V3.2.0

Download PDF

Document Feedback
  1. Documentation Center
  2. OceanBase Developer Center
  3. V4.4.2

Automatic authorization

Last Updated:2026-09-03 09:11:18

Background information
Create an automatic authorization rule
View automatic authorization rules
Automatic authorization rule list
View details of a rule
Edit a rule
Delete a rule
References

This topic describes how to create and manage automatic authorization rules.

Background information

OceanBase Developer Center (ODC) allows system administrators to define automatic authorization rules. System administrators can create, modify, view, and disable automatic authorization rules.

The automatic authorization feature automatically grants roles or permissions to users whose names, departments, or login methods meet specific conditions when they are being created or log in for the first time, to avoid redundant authorization operations.

This topic describes how to create an automatic authorization rule named grant system_admin for deptB, which automatically grants the system_admin role to a user whose username in memberOf.department contains deptB.

Create an automatic authorization rule

  1. Integrate OAuth 2.0 with ODC and authorize login to ODC. Assume that the OAuth 2.0 system returns the following data structure:

    {
      "id": 1,
      "name": "username",
      "mail": "example@email.com",
      "memberOf": {
        "department": [
          {
            "name": "deptA",
            "description": "this is a department"
          },
          {
            "name": "deptB",
            "description": "this is a department"
          }
        ],
        "extra": "some other info"
      }
    }
    

    You can use different expressions to obtain corresponding values from this data structure. The following table shows sample expressions and the corresponding values returned.

    Expression
    Result
    id 1
    memberOf.department[0].name deptA
    memberOf.department[*].name ["deptA", "deptB"]
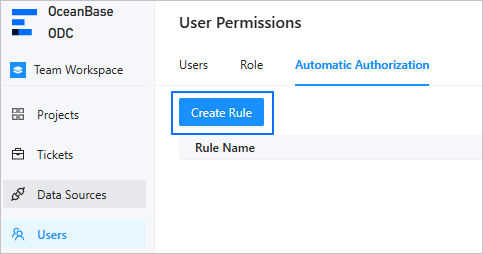
  2. Log in to Web ODC with a third-party account. In the left-side navigation pane of the project collaboration window, choose Users > Automatic Authorization > Create Rule.
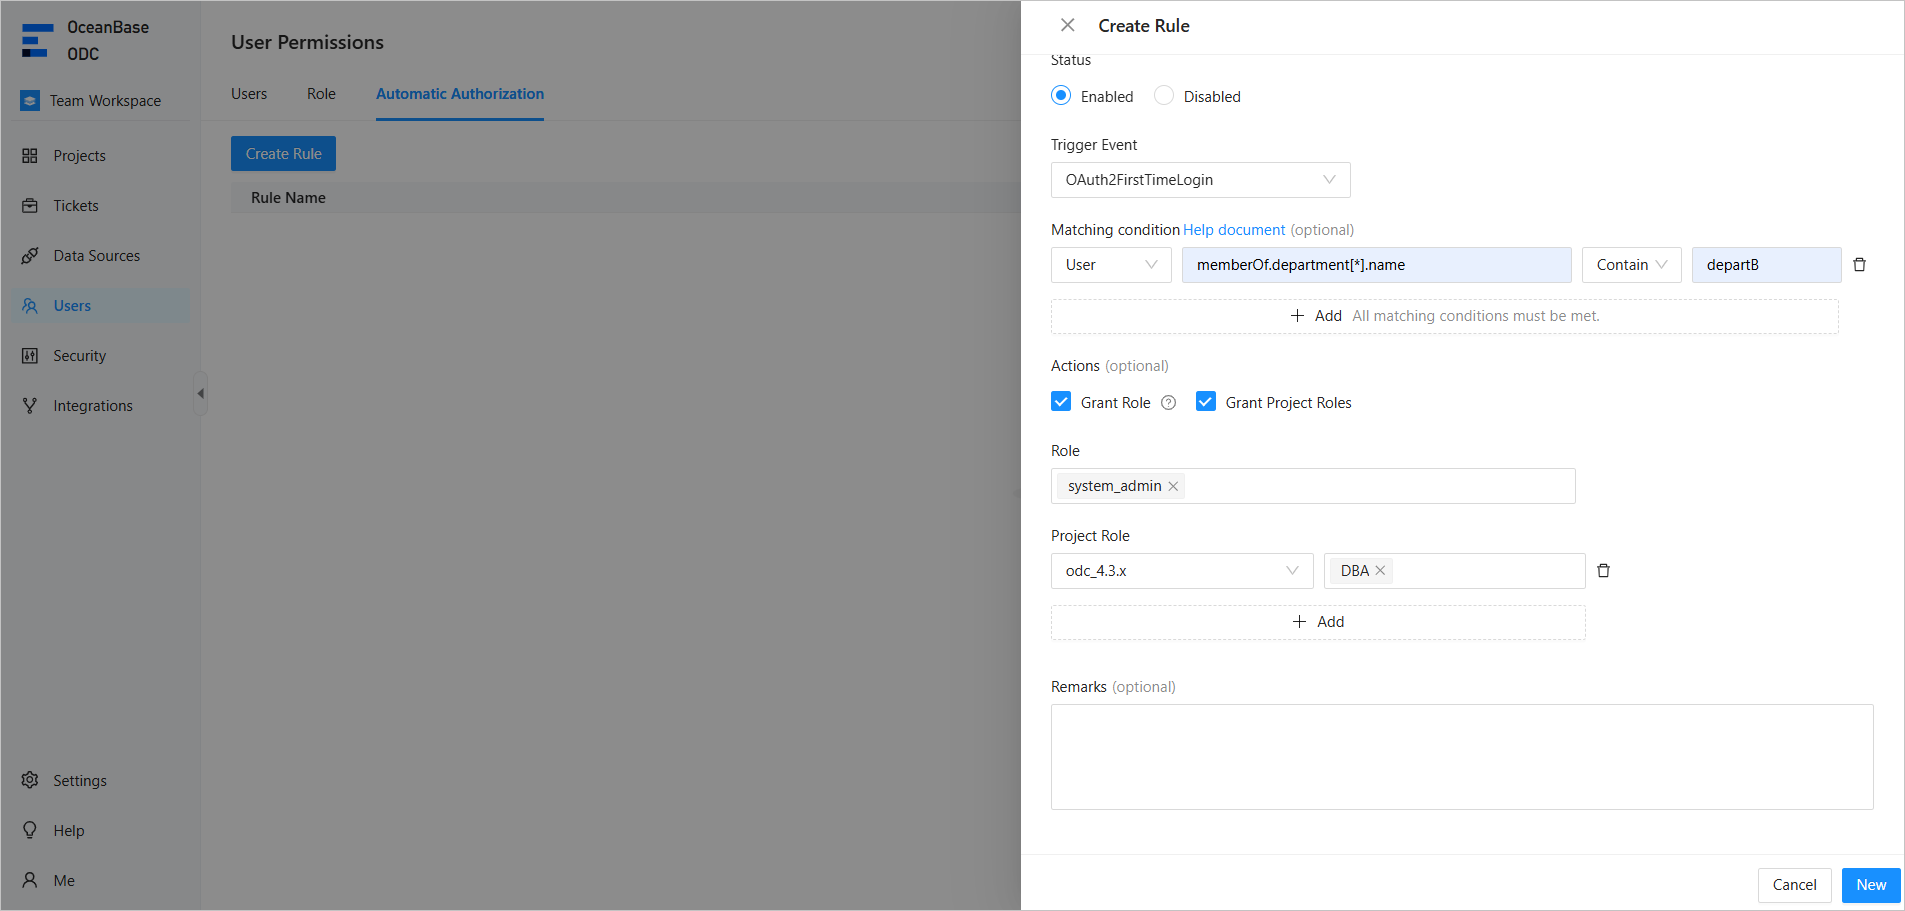
  3. Specify the following parameters in the Create Rule panel.
    Parameter
    Description
    Rule Name The name of the rule, which must be unique.
    Status Select Enabled or Disabled.
    By default, the status of the rule is Enabled. You can set it to Disabled as needed. A disabled rule cannot be accessed.
    Trigger Event Select a trigger event. Only built-in events are available. Different events correspond to different trigger occasions.
    Matching Condition (Optional) Click Add and specify the following four fields:
    • Object: stores the trigger condition and the information required for executing the action. It can be a complex nested object such as an array, a list, or a map, or a simple object such as a string or a number.
    • Expression: the index of the target in the object. Different types of objects use different indexing methods.
    • Operation: the supported operation, such as "Contain", "Match", or "Equal".
    • Value: the target value.

      Note

      • If you do not specify the matching condition, the action is unconditionally executed when the selected event is triggered.
      • If you select Match for the Operation field of the Matching Condition parameter, the value must be a regular expression.
    Actions (Optional) Select Grant Role and/or Grant Project Roles and specify the role name and/or project role name.

    Note

    If you do not specify the action, no action is executed regardless of whether the matching condition is met.

    Remarks (Optional) The description of the rule.
  4. After you specify the preceding information, click Create in the lower-right corner of the panel.

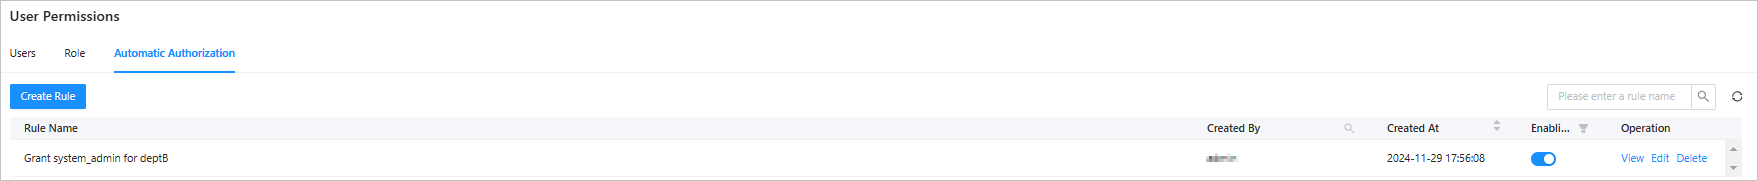
  5. After the rule is created, you can view the rule in the rule list.
View automatic authorization rules

Automatic authorization rule list

The following table describes the provided basic information of automatic authorization rules in the list.

Column
Description
Rule Name The name of the rule.
Created By The name of the user who created the rule.
You can click the search icon Search to search for rules created by a specific user.
Created At The time when the rule was last edited.
You can sort rules in ascending or descending order of creation time.
Enabling Status The status of the rule. Valid values: Enabled and Disabled.
You can click the filter icon Filter to filter rules by status.
Operation You can view, edit, and delete rules.

View details of a rule

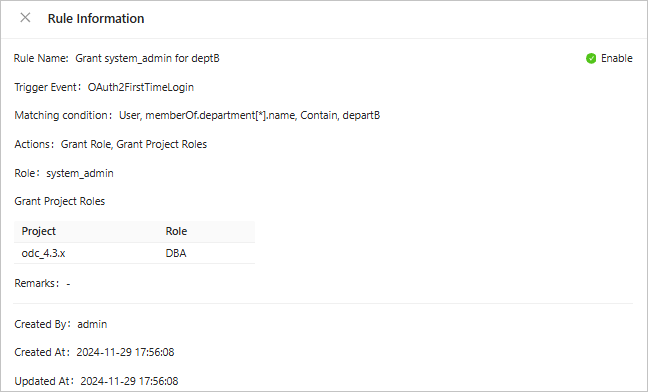
In the Operation column, click View. The Rule Information panel appears. The following information is displayed in the panel.

Information
Description
Rule information Displays the information you specified when you created the rule, such as Rule Name, Trigger Event, Matching Condition, Actions, Role, Grant Project Role, and Remarks.
Operation information Displays information in fields such as Created By, Created At, and Updated At.

Edit a rule

In the Operation column, click Edit. The Edit Rule panel appears.

The Edit Rule panel displays all the fields you specified when you created the rule. You can modify the fields as needed.

Delete a rule

In the Operation column, click Delete to delete an automatic authorization rule.

References

  • Users and roles

  • Login integration

Previous topic

Users and roles
Last

Next topic

Apply for project permissions
Next
on this page
Background information
Create an automatic authorization rule
View automatic authorization rules
Automatic authorization rule list
View details of a rule
Edit a rule
Delete a rule
References